Governance
Configure fix approvals, protected paths, and account settings in one place.
Counterswarm combines deep context from code to production with autonomous AI agents that continuously discover, fix, and prevent security risks.
Dependency Firewall is designed to assess packages in supported, configured installation paths. Security Reviewer analyzes connected human and AI-generated code changes for potential vulnerabilities and exposed credentials.
Code Scanner reasons across business logic, data flow, and exploit chains to uncover issues other tools miss.
Agentic Pentester can test supported findings against a configured, verified application. Security Reviewer can prepare draft pull requests for your team to review.
Agentic Pentester automatically re-runs runtime tests after every merge to verify fixes in your running application.
Find real vulnerabilities by tracing business logic, data flows, and cross-service interactions across your codebase.
Counterswarm investigates business logic and data flows, prioritizing findings with supporting evidence.
Detect malicious behavior before it spreads through your environment.
Confirm which vulnerabilities are exploitable by testing your running application with real attack paths.
Counterswarm tests your running applications and automatically re-tests fixes at runtime after every merge.
Prioritize dependency risk using package versions, advisories, and available usage evidence.
Counterswarm uses dependency versions and import evidence to help prioritize vulnerabilities relevant to your application.
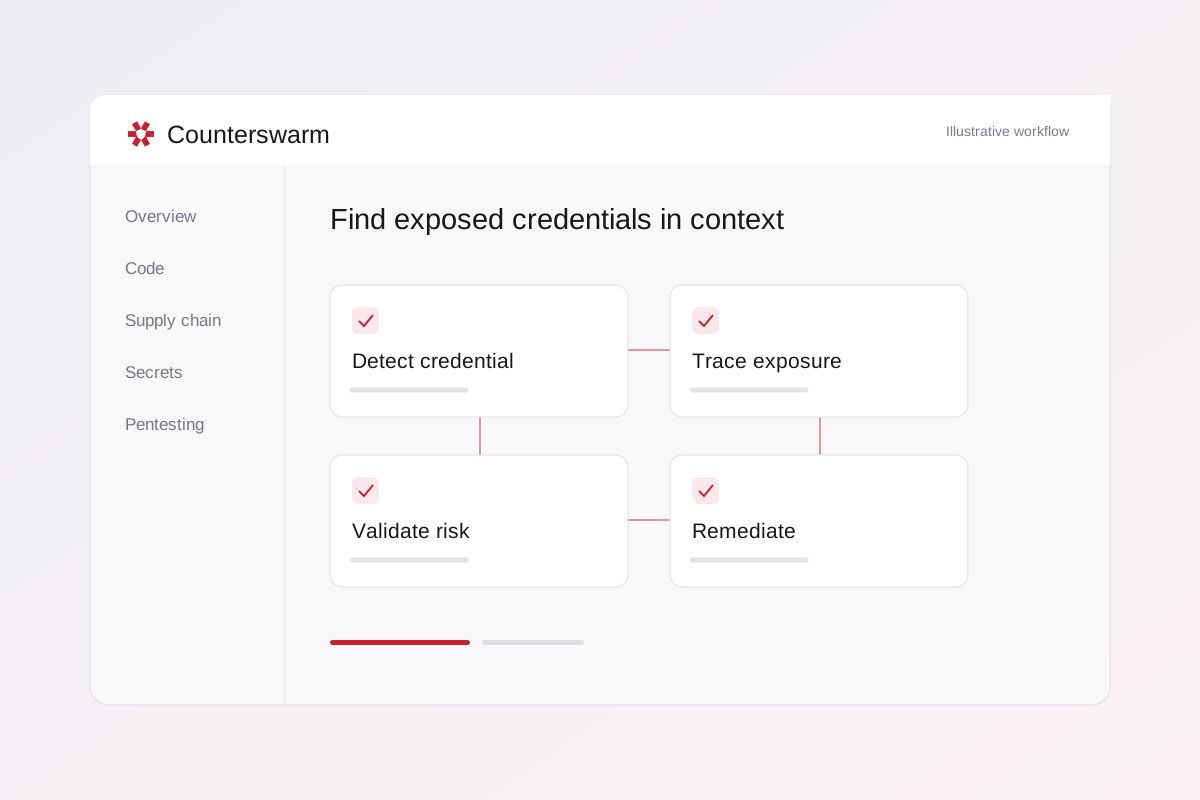
Detect and validate credentials across your codebase, CI/CD pipelines, and runtime environments.
Configure fix approvals, protected paths, and account settings in one place.
Review findings and fix activity in one place, with finding exports available.
Review recorded scan activity and finding state changes.
Account membership controls access to connected repositories and findings.
Bring your own encryption key. Your data stays encrypted with keys you control.