Discover hidden backdoors
Counterswarm identifies code paths where specific inputs return authentication tokens or privileged access. These exposures live inside business logic, not configuration files.
Counterswarm identifies potential exposed credentials using repository and provider-format context, helping your team investigate and remediate exposures.
Counterswarm identifies code paths where specific inputs return authentication tokens or privileged access. These exposures live inside business logic, not configuration files.
Counterswarm scans repository files and git history for potential exposed credentials, helping your team investigate long-standing exposures.
Review potentially sensitive values in connected repository files, using available findings to guide investigation and remediation.
Counterswarm combines secret-detection patterns with provider-format and code context to help distinguish potential credentials from public values and placeholders.
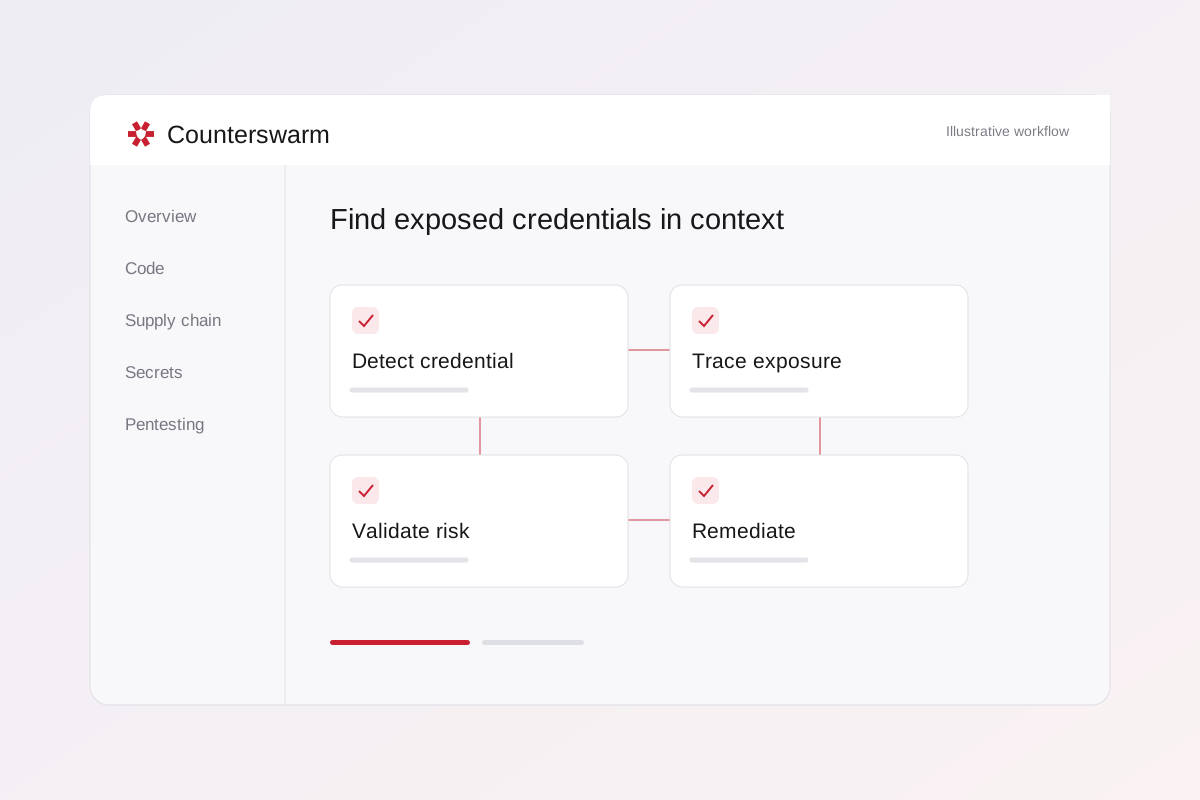
Potential exposed credentials are identified with provider-format and repository context, helping your team investigate and rotate them.
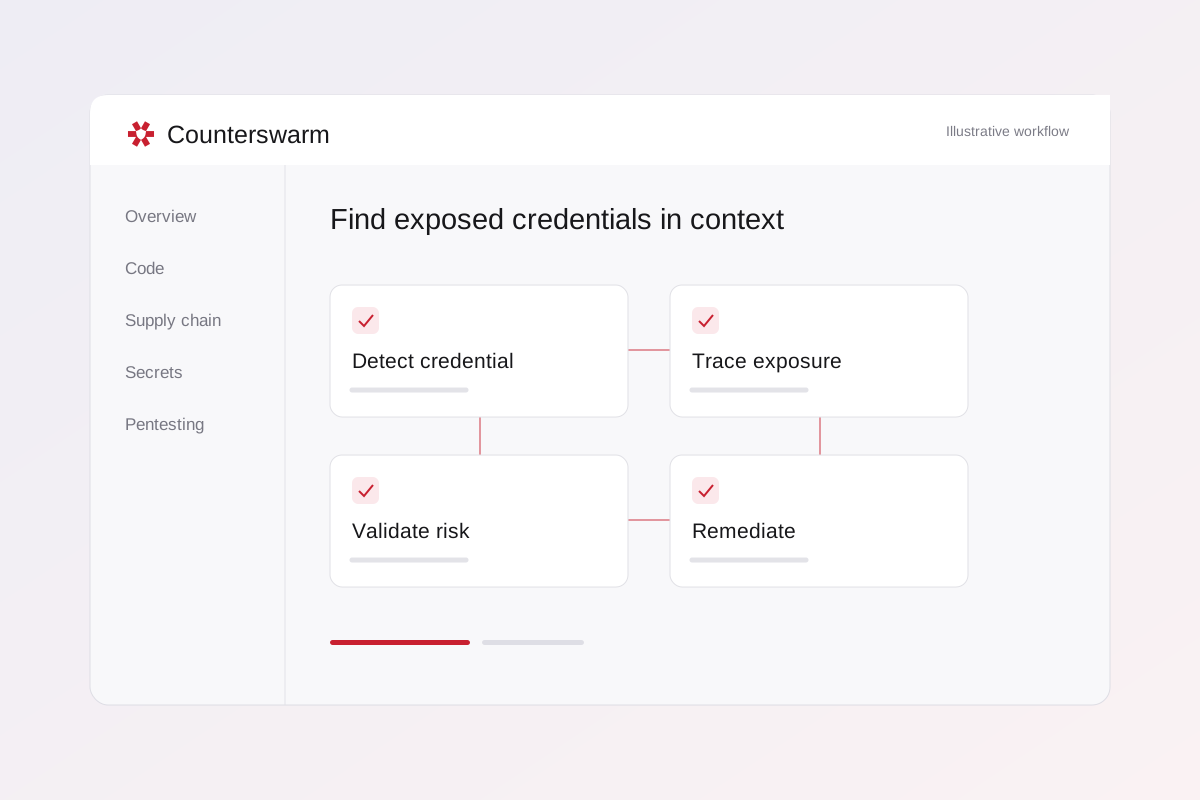
Counterswarm scans connected repository files and git history for potential exposed credentials, with scan coverage and limits reported for review.
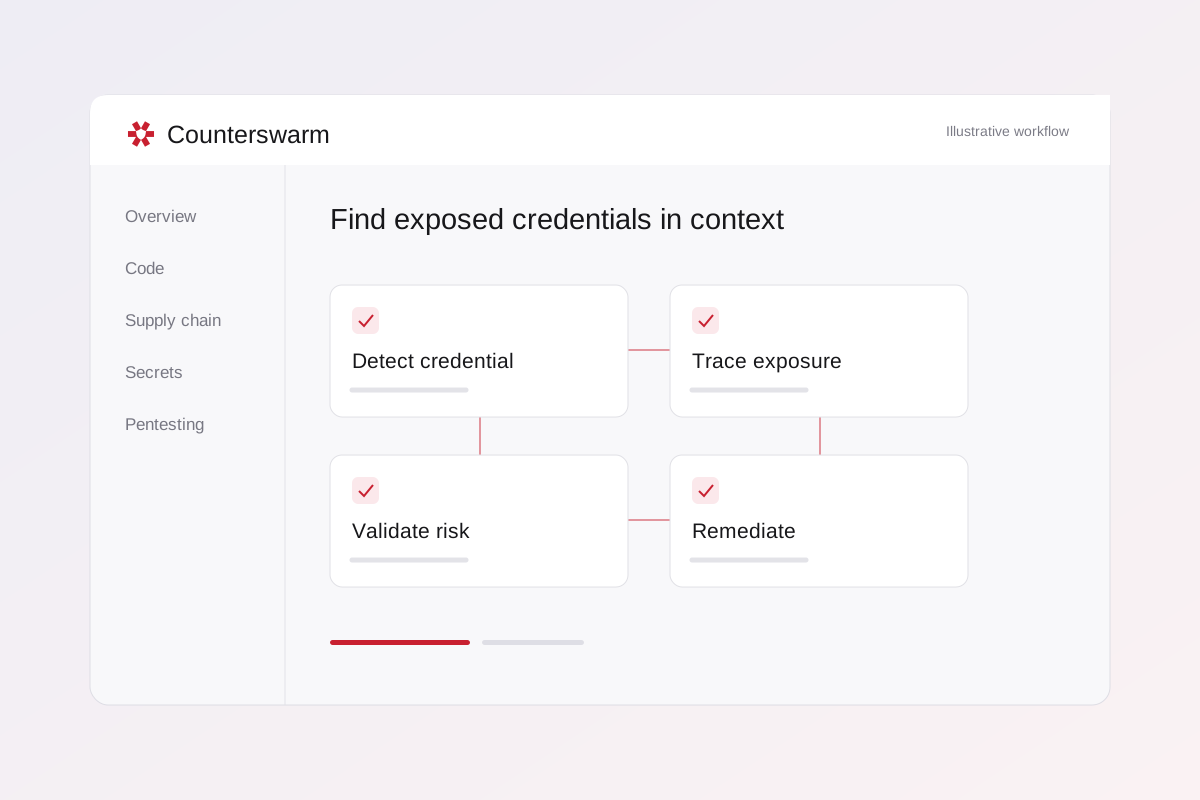
PR scans run in your existing pipeline, flagging new secrets before they reach production.
Findings surface as PR comments with one click to view full context and remediation steps.
Deep scans cover the full repo and PR scans catch what is being introduced, all in one tool.
Each finding shows where the secret is used across your codebase, so your team rotates it safely.
Find real vulnerabilities by tracing business logic, data flows, and cross-service interactions across your codebase.
Counterswarm investigates business logic and data flows, prioritizing findings with supporting evidence.
Detect malicious behavior before it spreads through your environment.
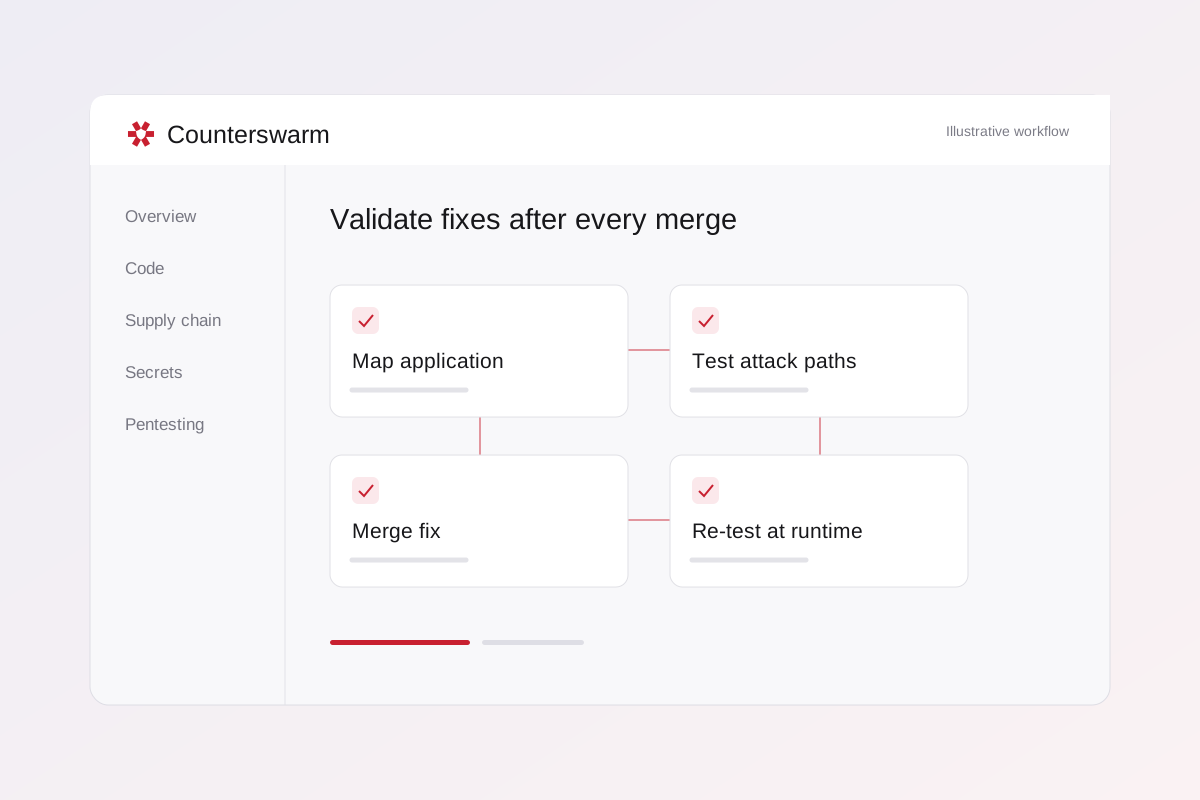
Confirm which vulnerabilities are exploitable by testing your running application with real attack paths.
Counterswarm tests your running applications and automatically re-tests fixes at runtime after every merge.
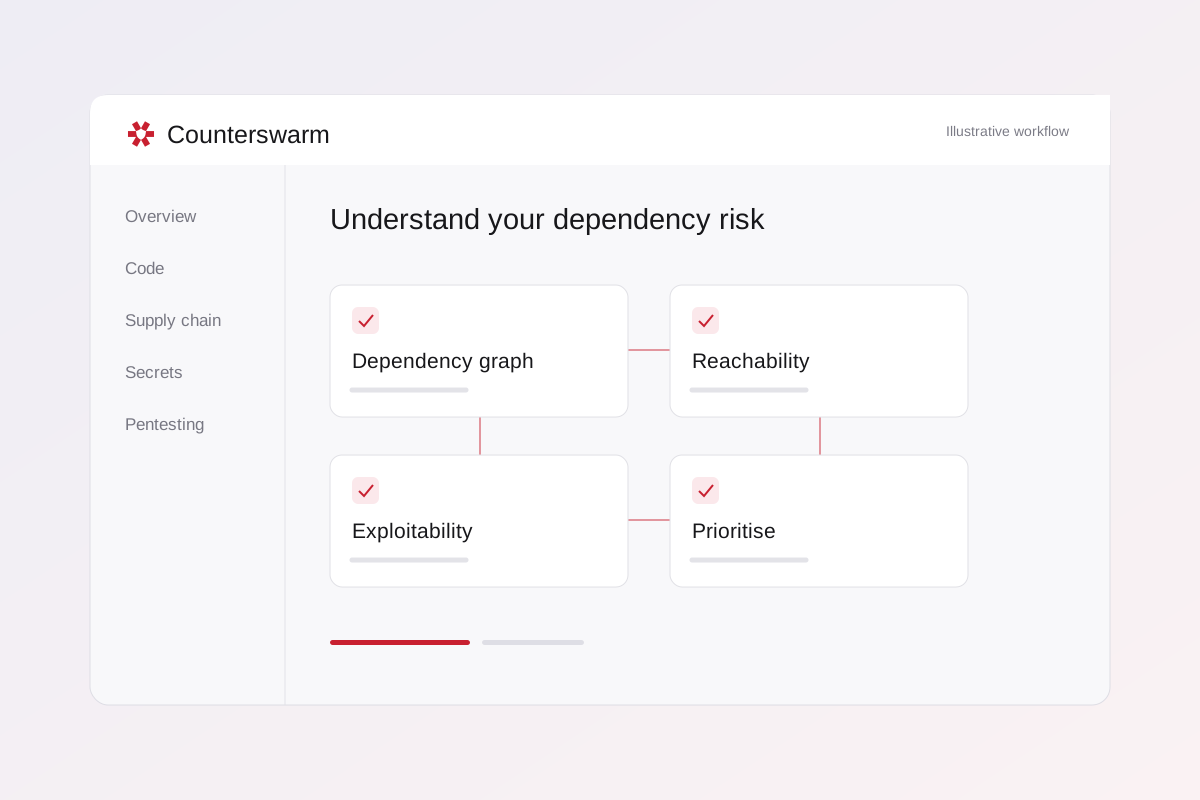
Prioritize dependency risk using package versions, advisories, and available usage evidence.
Counterswarm uses dependency versions and import evidence to help prioritize vulnerabilities relevant to your application.