Stop unauthorized access before it ships
Counterswarm catches broken authorization, privilege escalation, IDOR, and subscription tier bypasses by reasoning about what your code is supposed to do
We understand your code like a Security Engineer, tracing business logic, mapping cross-service data flows, and surfacing real vulnerabilities, fixing them autonomously.
Counterswarm catches broken authorization, privilege escalation, IDOR, and subscription tier bypasses by reasoning about what your code is supposed to do
Counterswarm maps data flows across service boundaries, exposing attack paths that only exist between components—where an input in one service reaches a vulnerable sink in another.
Counterswarm connects individual low-severity findings into exploitable paths by mapping how weak points chain together through your application’s data flows and control logic.
Surface broken authorization, privilege escalation, and logic flaws by analyzing data flow, service interactions, and runtime behavior across your codebase.
Reduce triage noise with evidence trails and exploitation conditions. When scoped runtime testing is enabled and configured, supported checks can test findings against your application.
Ship fixes faster with pull request comments that match your conventions. Developers review and merge without context-switching or manual remediation.
Analyze your entire codebase to surface the full landscape of vulnerabilities.
Review connected code changes and surface potential vulnerabilities with supporting evidence.
Findings surface as PR comments with one-click access to full context and generated fixes.
Review findings and record feedback to guide future triage.
Detect malicious behavior before it spreads through your environment.
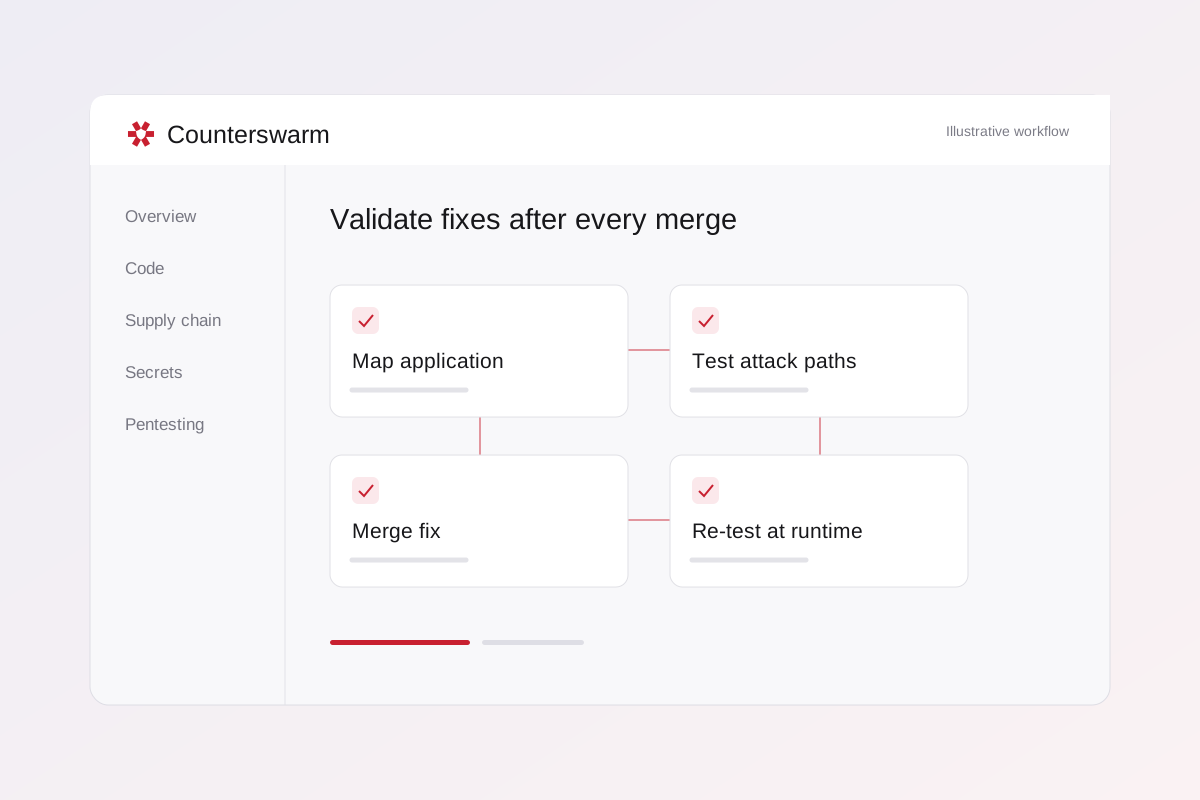
Confirm which vulnerabilities are exploitable by testing your running application with real attack paths.
Counterswarm tests your running applications and automatically re-tests fixes at runtime after every merge.
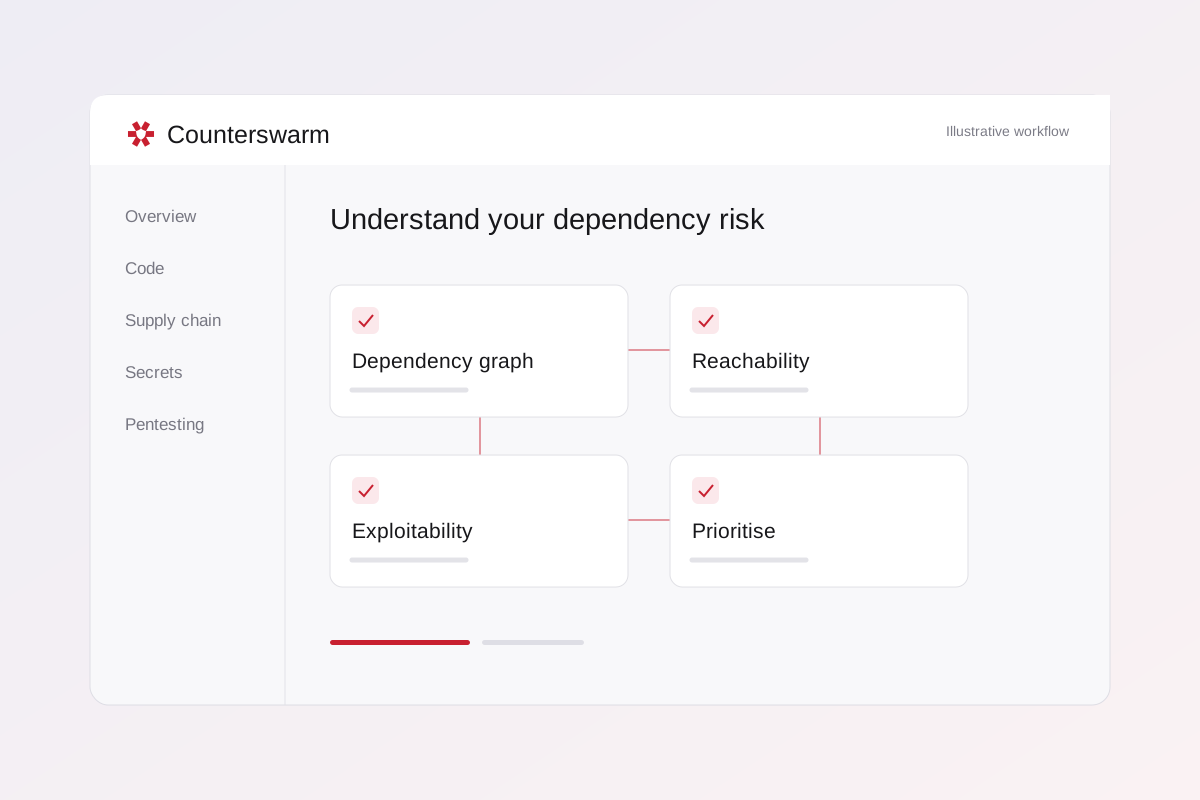
Prioritize dependency risk using package versions, advisories, and available usage evidence.
Counterswarm uses dependency versions and import evidence to help prioritize vulnerabilities relevant to your application.
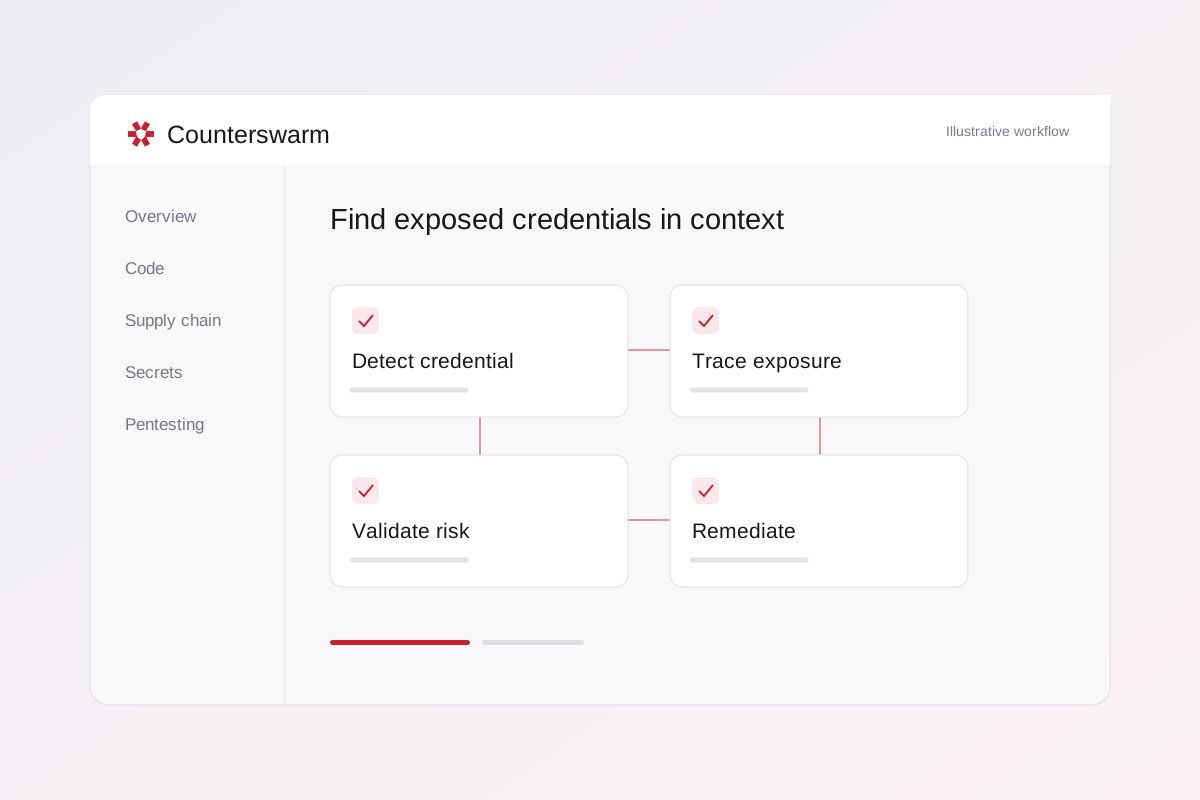
Detect and validate credentials across your codebase, CI/CD pipelines, and runtime environments.