Business Context
Add context about each repository in plain language: what the service does, who uses it, and what it handles.
Multiple LLMs run in parallel to build a structural understanding of how your system works.
Dependency Firewall is designed to assess packages in supported, configured installation paths. Security Reviewer analyzes connected human and AI-generated code changes for potential vulnerabilities and exposed credentials.
Code Scanner reasons across business logic, data flow, and exploit chains to uncover issues other tools miss.
Agentic Pentester can test supported findings against a configured, verified application. Security Reviewer can prepare draft pull requests for your team to review.
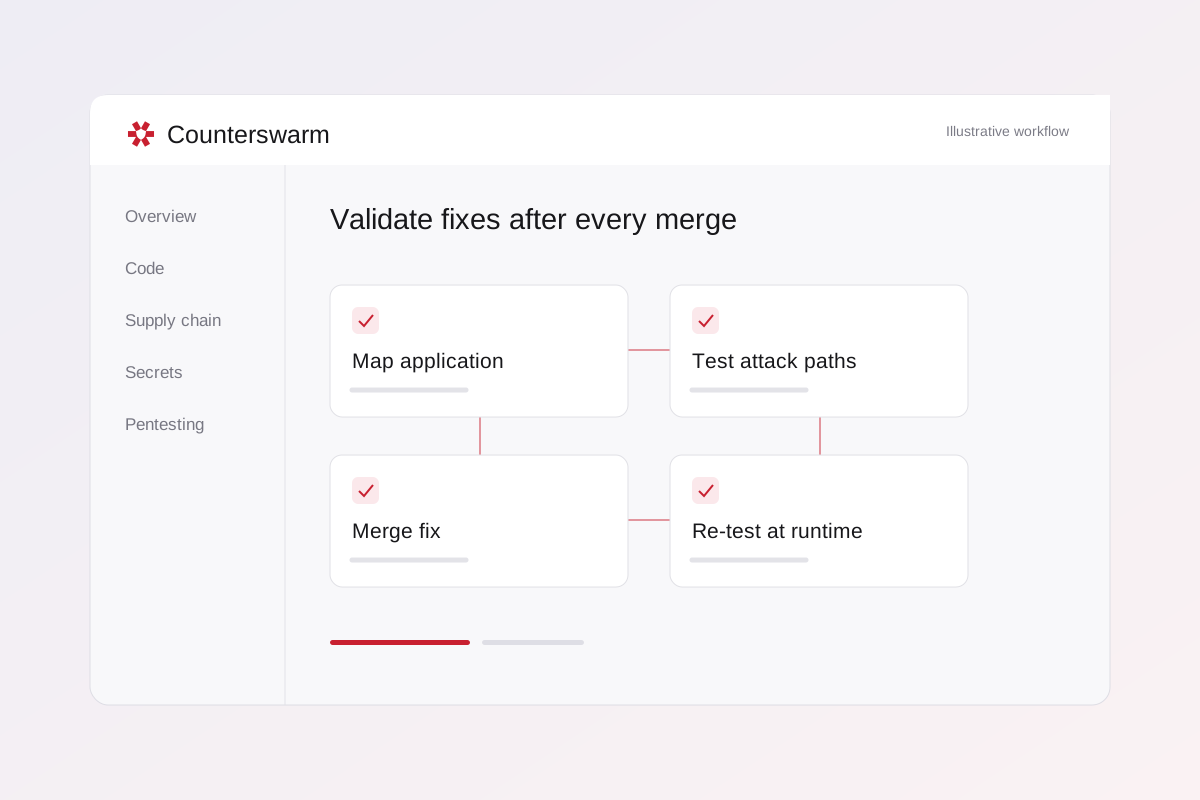
Agentic Pentester automatically re-runs runtime tests after every merge to verify fixes in your running application.
Counterswarm uses repository context, code analysis, and available dependency evidence to investigate potential security issues.
Counterswarm improves over time by learning from developer feedback on its recommendations. Adjustments are visible on the platform so you can track what the system has learned.
Review findings by repository and severity, along with scan activity and reported coverage across connected repositories.
Add context about each repository in plain language: what the service does, who uses it, and what it handles.
Write detection rules in plain English and Counterswarm applies them across your codebase.
Query findings, trigger scans, and integrate Counterswarm into your own workflows and tooling programmatically.
Find real vulnerabilities by tracing business logic, data flows, and cross-service interactions across your codebase.
Counterswarm investigates business logic and data flows, prioritizing findings with supporting evidence.
Detect malicious behavior before it spreads through your environment.
Confirm which vulnerabilities are exploitable by testing your running application with real attack paths.
Counterswarm tests your running applications and automatically re-tests fixes at runtime after every merge.
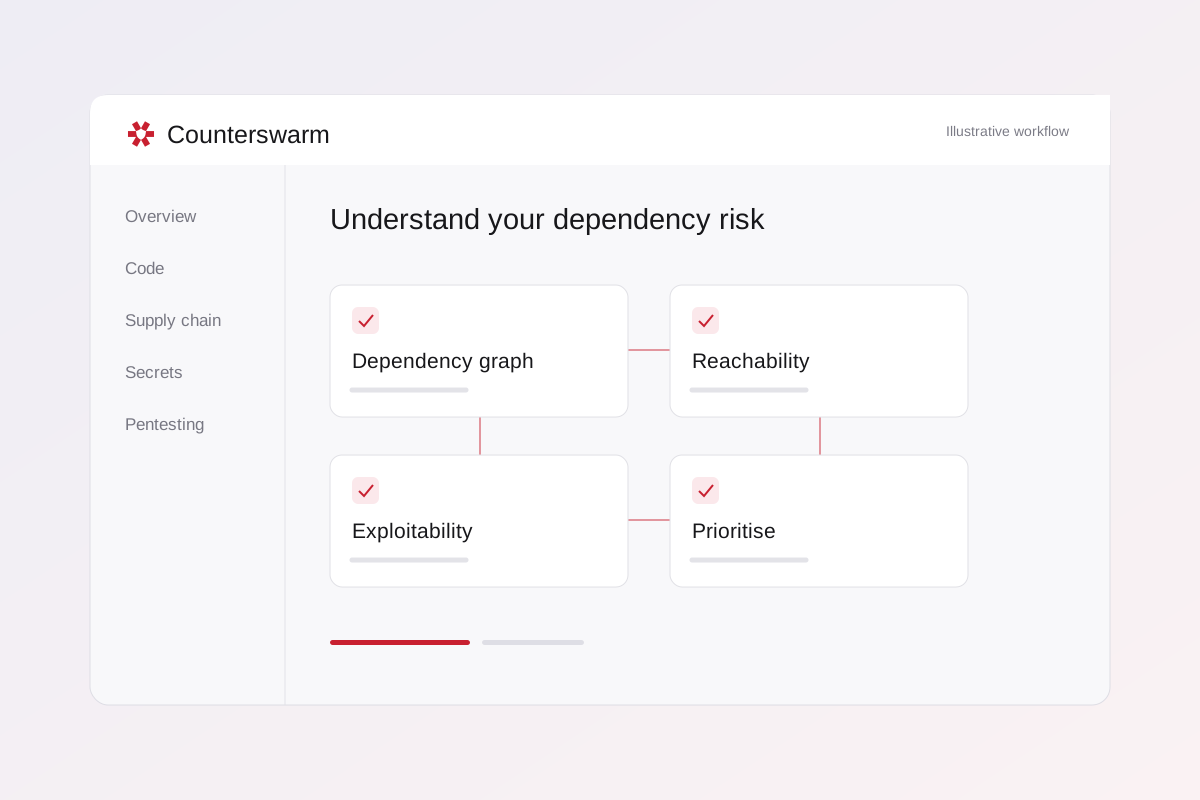
Prioritize dependency risk using package versions, advisories, and available usage evidence.
Counterswarm uses dependency versions and import evidence to help prioritize vulnerabilities relevant to your application.
Detect and validate credentials across your codebase, CI/CD pipelines, and runtime environments.